News Security CVE-2026-50656 “RoguePlanet” in Microsoft Defender: what’s known and how to prepare June 22, 2026 / June 22, 2026 by Alex Mira | Leave a Comment Microsoft is preparing a fix for CVE-2026-50656 (“RoguePlanet”), an elevation-of-privilege issue in Microsoft Defender’s engine. Here’s what’s confirmed, what’s still unclear, and how to prepare while waiting for the patch. Read more » CVE-2026-50656 Elevation of Privilege Microsoft Defender RoguePlanet Windows security Zero-day
News Security ShapedPlugin supply-chain compromise: backdoored Pro updates via official channels (CVE-2026-10735) June 22, 2026 / June 22, 2026 by Alex Mira | Leave a Comment Wordfence and BleepingComputer report a ShapedPlugin supply‑chain compromise that backdoored Pro updates via official channels (CVE-2026-10735). Free repo builds were reported clean. Read more » 2FA CVE-2026-10735 incident response ShapedPlugin Supply chain attack WooCommerce WordPress security
News Security Active exploits hit Gravity SMTP (CVE-2026-4020); Avada Builder critical bug patched (CVE-2026-8713) June 22, 2026 / June 22, 2026 by Alex Mira | Leave a Comment Active exploitation hits Gravity SMTP (CVE-2026-4020) while Avada Builder’s critical file deletion bug (CVE-2026-8713) is patched. Update now, check logs for the Gravity SMTP REST endpoint, and consult Wordfence’s indicators for targeted IPs. Read more » Avada Builder CVE-2026-4020 CVE-2026-8713 Gravity SMTP incident response Plugin vulnerability WordPress security
News Anthropic disables Fable 5 and Mythos 5 after U.S. export control directive June 13, 2026 / June 13, 2026 by Alex Mira | Leave a Comment Anthropic has disabled access to Fable 5 and Mythos 5 after a U.S. export control directive tied to national security. Earlier Claude models remain available while the company works on next steps. Read more » AI models Anthropic compliance export controls policy security
News Security CVE-2026-10795: Authentication bypass in UpdraftPlus impacts sites connected to UpdraftCentral June 12, 2026 / June 12, 2026 by Alex Mira | Leave a Comment CVE-2026-10795 is a high-severity authentication bypass in UpdraftPlus fixed in 1.26.5, exploitable only on sites previously connected to UpdraftCentral. Read more » CVE-2026-10795 Security Patch UpdraftCentral UpdraftPlus vulnerability wordpress
News Notepad++ path traversal bypass can execute commands without a prompt (CVE-2026-52884) June 12, 2026 / June 12, 2026 by Alex Mira | Leave a Comment A Notepad++ advisory (CVE-2026-52884) describes a path traversal bypass that can execute commands without the editor’s usual confirmation dialog. Attack paths involve tampering with shortcuts.xml or redirecting the settings directory. Patch status is unclear; monitor the advisory and handle configuration files with care. Read more » Configuration Files CVE-2026-52884 GitHub Security Advisory Notepad++ Path Traversal Windows security
News Windows Windows 11’s Low Latency Profile arrives with June’s update: what it changes and how to turn it on June 12, 2026 / June 12, 2026 by Alex Mira | Leave a Comment Microsoft’s June 2026 Patch Tuesday adds Windows 11’s Low Latency Profile for snappier Start, Search, and app launches. It’s rolling out gradually, but you can enable it now with ViVeTool and verify the CPU burst in Task Manager. Read more » KB5094126 Low Latency Profile patch tuesday performance Task Manager ViVeTool Windows 11
News Microsoft patches actively exploited Exchange Server zero-day (CVE-2026-42897) June 10, 2026 / June 10, 2026 by Alex Mira | Leave a Comment Microsoft patched an actively exploited Exchange Server zero-day (CVE-2026-42897) that enables XSS against Outlook Web Access users. Admins should install June 2026 updates promptly and keep EEMS mitigations enabled. Read more » CISA KEV CVE-2026-42897 Microsoft Exchange Server Outlook Web Access XSS Zero-day
News CVE-2026-3300: Active exploits target Everest Forms Pro’s Complex Calculation feature June 7, 2026 / June 7, 2026 by Alex Mira | Leave a Comment CVE-2026-3300 in Everest Forms Pro is under active exploitation. The bug enables unauthenticated remote code execution via the Complex Calculation feature. Update to 1.9.13, audit admin users for “diksimarina,” and review logs for the IPs cited by Wordfence. Read more » CVE-2026-3300 Everest Forms Pro Plugin vulnerability Remote code execution security wordpress
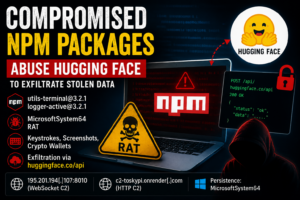
News Security Compromised npm Packages Abuse Hugging Face as Exfiltration Infrastructure June 4, 2026 / June 4, 2026 by Corentin C | Leave a Comment Microsoft Threat Intelligence has warned that compromised npm packages utils-terminal@3.2.1 and logger-active@3.2.1 are deploying the MicrosoftSystem64 RAT. The malware captures keystrokes, screenshots, and crypto wallet credentials while abusing Hugging Face infrastructure as an exfiltration channel. Read more » huggingface MicrosoftSystem64 npm rat security trojan