News Security Zoom patches critical Windows account takeover flaw (CVE-2026-53412) and related privilege escalation issue July 20, 2026 / July 20, 2026 by Alex Mira | Leave a Comment Zoom fixed a critical Windows account takeover flaw (CVE-2026-53412) and a related privilege escalation issue (CVE-2026-53411). Update Windows clients, VDI deployments, and the Meeting SDK without delay. Read more » CVE-2026-53411 CVE-2026-53412 Enterprise security Patch management VDI Windows security Zoom
News Security CVE-2026-25089 in Fortinet FortiSandbox: active exploitation confirmed, patch now and lock down access July 20, 2026 / July 20, 2026 by Alex Mira | Leave a Comment CISA confirmed active exploitation of CVE-2026-25089 in Fortinet FortiSandbox. Here’s what’s affected, the fixed versions, and practical steps to patch and lock down access—plus what remains uncertain. Read more » CISA KEV Command Injection CVE-2026-25089 Fortinet FortiSandbox patch tuesday Vulnerability Management
News Security Patch now: WordPress Core “wp2shell” chain (CVE-2026-60137, CVE-2026-63030) July 20, 2026 / July 20, 2026 by Alex Mira | Leave a Comment Two WordPress Core bugs—CVE-2026-60137 and CVE-2026-63030—can be chained for pre-auth RCE on specific versions. Public PoCs exist. Update to 7.0.2 or 6.9.5 now. Read more » CVE-2026-60137 CVE-2026-63030 Remote code execution Security Update SQL injection wordpress
News Security Linux kernel privilege-escalation bugs touch cloud and industrial systems: what’s confirmed June 27, 2026 / June 27, 2026 by Alex Mira | Leave a Comment Multiple Linux kernel privilege-escalation bugs now documented by Google Cloud and CISA affect cloud workloads and at least one industrial product line. Here’s what’s confirmed and what to do next based on the advisories. Read more » CISA Cloud security cve Google Cloud ICS security Linux kernel Privilege escalation
News Security FFmpeg patches “PixelSmash” in MagicYUV: what users of media apps should know June 23, 2026 / June 23, 2026 by Alex Mira | Leave a Comment FFmpeg fixed “PixelSmash” (CVE-2026-8461) in the MagicYUV decoder, a flaw that can crash applications and, under specific conditions, enable RCE. A separate RASC decoder bug (CVE-2026-12706) can also cause crashes when parsing malicious AVI files. Read more » CVE-2026-12706 CVE-2026-8461 FFmpeg Jellyfin MagicYUV Media security Supply chain Vulnerabilities
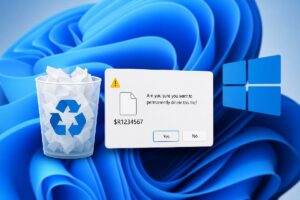
News Windows Recycle Bin delete prompts are showing the wrong names after June’s Windows updates, but your files are fine June 22, 2026 / June 22, 2026 by Alex Mira | Leave a Comment June’s Windows updates can make Recycle Bin delete prompts show internal names like $Rxxxxx. Microsoft says it’s a dialog-only glitch—files list and restore correctly. Read more » IT admin KB5094126 microsoft patch tuesday Recycle Bin Windows 10 Windows 11 Windows Server
News Windows Windows 11 26H2 is a light, predictable update arriving this fall June 22, 2026 / June 22, 2026 by Alex Mira | Leave a Comment Microsoft confirms Windows 11 26H2 for fall 2026 as a small enablement update over 25H2, with unchanged hardware requirements, clear support timelines, and Search tweaks in Insider testing. Read more » enablement package IT administration microsoft Search Windows 11 Windows Insider Windows Update
News Security CVE-2026-35273: Critical unauthenticated RCE risk in Oracle PeopleSoft PeopleTools June 22, 2026 / June 22, 2026 by Alex Mira | Leave a Comment Oracle warns of CVE-2026-35273, a critical unauthenticated RCE risk in PeopleSoft PeopleTools 8.61/8.62. Mitigations are available now and immediate action is advised amid reports of active exploitation. Read more » CVE-2026-35273 Mitigation Oracle PeopleSoft PeopleTools Remote code execution Security Alert
News Security CVE-2026-10557: Hard‑coded MQTT credentials expose Yarbo robot telemetry and commands June 22, 2026 / June 22, 2026 by Alex Mira | Leave a Comment CVE-2026-10557 details hard‑coded, shared MQTT credentials in Yarbo’s mobile apps that expose fleet‑wide robot telemetry and enable command publishing using only a serial number. CISA rates it Critical (CVSS 9.8). Here’s what’s confirmed, why it matters, and prudent steps until vendor guidance arrives. Read more » cve ICS IoT security Mobile apps MQTT privacy vulnerability
News Security CVE-2026-54420: Active exploitation of LiteSpeed’s cPanel plugin and what hosting admins should do now June 22, 2026 / June 22, 2026 by Alex Mira | Leave a Comment CVE-2026-54420 in LiteSpeed’s cPanel plugin is under active exploitation. Shared hosting admins should update to the fixed versions, review logs, and prioritize KEV patching. Read more » CISA KEV CloudLinux cpanel CVE-2026-54420 LiteSpeed Privilege escalation Shared hosting