News Security FFmpeg patches “PixelSmash” in MagicYUV: what users of media apps should know June 23, 2026 / June 23, 2026 by Alex Mira | Leave a Comment FFmpeg fixed “PixelSmash” (CVE-2026-8461) in the MagicYUV decoder, a flaw that can crash applications and, under specific conditions, enable RCE. A separate RASC decoder bug (CVE-2026-12706) can also cause crashes when parsing malicious AVI files. Read more » CVE-2026-12706 CVE-2026-8461 FFmpeg Jellyfin MagicYUV Media security Supply chain Vulnerabilities
News Security CVE-2026-35273: Critical unauthenticated RCE risk in Oracle PeopleSoft PeopleTools June 22, 2026 / June 22, 2026 by Alex Mira | Leave a Comment Oracle warns of CVE-2026-35273, a critical unauthenticated RCE risk in PeopleSoft PeopleTools 8.61/8.62. Mitigations are available now and immediate action is advised amid reports of active exploitation. Read more » CVE-2026-35273 Mitigation Oracle PeopleSoft PeopleTools Remote code execution Security Alert
News Security CVE-2026-10557: Hard‑coded MQTT credentials expose Yarbo robot telemetry and commands June 22, 2026 / June 22, 2026 by Alex Mira | Leave a Comment CVE-2026-10557 details hard‑coded, shared MQTT credentials in Yarbo’s mobile apps that expose fleet‑wide robot telemetry and enable command publishing using only a serial number. CISA rates it Critical (CVSS 9.8). Here’s what’s confirmed, why it matters, and prudent steps until vendor guidance arrives. Read more » cve ICS IoT security Mobile apps MQTT privacy vulnerability
News Security CVE-2026-54420: Active exploitation of LiteSpeed’s cPanel plugin and what hosting admins should do now June 22, 2026 / June 22, 2026 by Alex Mira | Leave a Comment CVE-2026-54420 in LiteSpeed’s cPanel plugin is under active exploitation. Shared hosting admins should update to the fixed versions, review logs, and prioritize KEV patching. Read more » CISA KEV CloudLinux cpanel CVE-2026-54420 LiteSpeed Privilege escalation Shared hosting
News Security CVE-2026-50656 “RoguePlanet” in Microsoft Defender: what’s known and how to prepare June 22, 2026 / June 22, 2026 by Alex Mira | Leave a Comment Microsoft is preparing a fix for CVE-2026-50656 (“RoguePlanet”), an elevation-of-privilege issue in Microsoft Defender’s engine. Here’s what’s confirmed, what’s still unclear, and how to prepare while waiting for the patch. Read more » CVE-2026-50656 Elevation of Privilege Microsoft Defender RoguePlanet Windows security Zero-day
News Security ShapedPlugin supply-chain compromise: backdoored Pro updates via official channels (CVE-2026-10735) June 22, 2026 / June 22, 2026 by Alex Mira | Leave a Comment Wordfence and BleepingComputer report a ShapedPlugin supply‑chain compromise that backdoored Pro updates via official channels (CVE-2026-10735). Free repo builds were reported clean. Read more » 2FA CVE-2026-10735 incident response ShapedPlugin Supply chain attack WooCommerce WordPress security
News Security Active exploits hit Gravity SMTP (CVE-2026-4020); Avada Builder critical bug patched (CVE-2026-8713) June 22, 2026 / June 22, 2026 by Alex Mira | Leave a Comment Active exploitation hits Gravity SMTP (CVE-2026-4020) while Avada Builder’s critical file deletion bug (CVE-2026-8713) is patched. Update now, check logs for the Gravity SMTP REST endpoint, and consult Wordfence’s indicators for targeted IPs. Read more » Avada Builder CVE-2026-4020 CVE-2026-8713 Gravity SMTP incident response Plugin vulnerability WordPress security
News Security CVE-2026-10795: Authentication bypass in UpdraftPlus impacts sites connected to UpdraftCentral June 12, 2026 / June 12, 2026 by Alex Mira | Leave a Comment CVE-2026-10795 is a high-severity authentication bypass in UpdraftPlus fixed in 1.26.5, exploitable only on sites previously connected to UpdraftCentral. Read more » CVE-2026-10795 Security Patch UpdraftCentral UpdraftPlus vulnerability wordpress
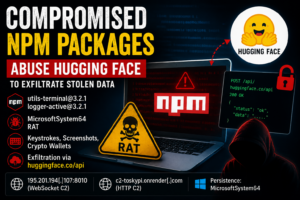
News Security Compromised npm Packages Abuse Hugging Face as Exfiltration Infrastructure June 4, 2026 / June 4, 2026 by Corentin C | Leave a Comment Microsoft Threat Intelligence has warned that compromised npm packages utils-terminal@3.2.1 and logger-active@3.2.1 are deploying the MicrosoftSystem64 RAT. The malware captures keystrokes, screenshots, and crypto wallet credentials while abusing Hugging Face infrastructure as an exfiltration channel. Read more » huggingface MicrosoftSystem64 npm rat security trojan
News Security Critical cPanel Vulnerability CVE-2026-41940 Actively Exploited: What Website Owners and Hosting Providers Need to Know May 4, 2026 / May 4, 2026 by Corentin C | Leave a Comment CVE-2026-41940 is a critical cPanel and WHM authentication bypass vulnerability actively exploited in the wild. Learn who is affected, what attackers can do, and how to patch. Read more » cpanel cve cve-2026-41940 security vulnerability web hosting